
The PHP vulnerabilities (php2shell): how Dixlase is responding
Hi, I'm Kashiwabara ("Kassy") at exc-D inc., the company behind Dixlase.
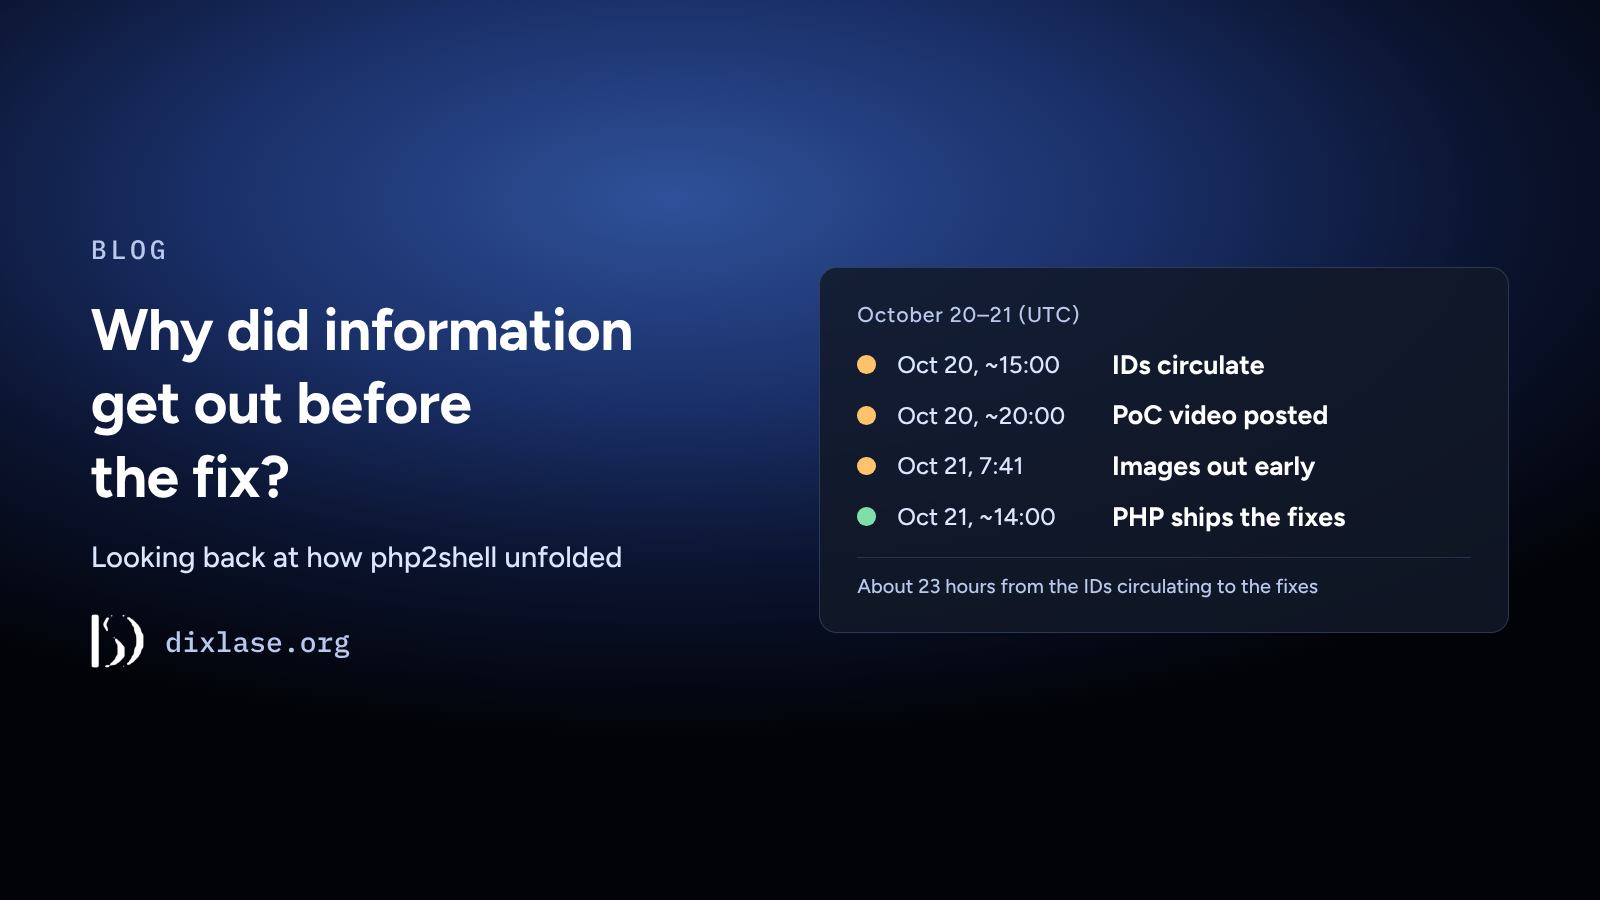
In October 21, 2026, two critical vulnerabilities in PHP itself were disclosed.
Dixlase runs on PHP, so this post covers what happened, how Dixlase has responded, and what we ask of everyone running Dixlase.
What happened
Two vulnerabilities were found in PHP itself: CVE-2026-109618 and CVE-2026-109619, also known as "php2shell."
PHP rates both at 9.2 on CVSS v4.0. They could let an attacker run code on a server remotely, without logging in.
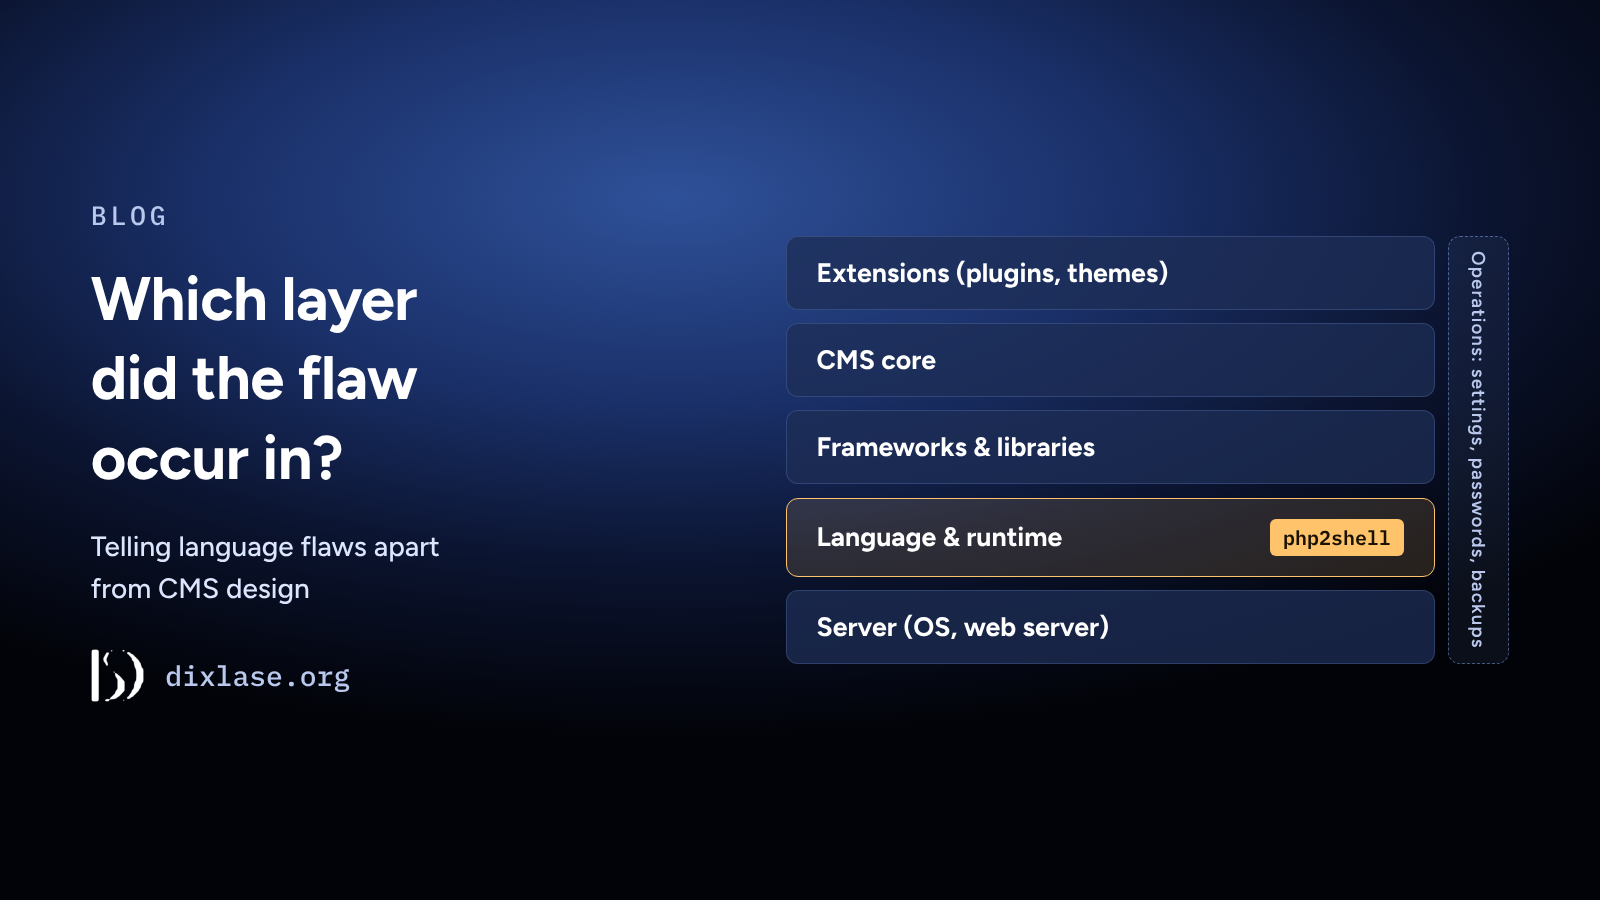
These vulnerabilities are in PHP itself. They are not a problem with any particular CMS or application.
Every PHP installation that handles web requests is affected.
On October 21, PHP released fixed versions (8.5.12, 8.4.27, 8.3.36, and 8.2.35).
Sources: PHP security advisory / The Hacker News / Help Net Security
What we did on Dixlase's servers
On October 22, we updated PHP on the servers that Dixlase runs to the fixed versions.
Are the Dixlase core or plugins affected?
These vulnerabilities are in PHP itself, not in the code of the Dixlase core or the official plugins and themes.
But because Dixlase runs on top of PHP, updating Dixlase alone won't fix them. You need to update PHP on your server.
What we ask you to do
Please update PHP to at least the following versions:
- On PHP 8.3: 8.3.36 or later
- On PHP 8.4: 8.4.27 or later
- On PHP 8.5: 8.5.12 or later
If you use the Docker installer
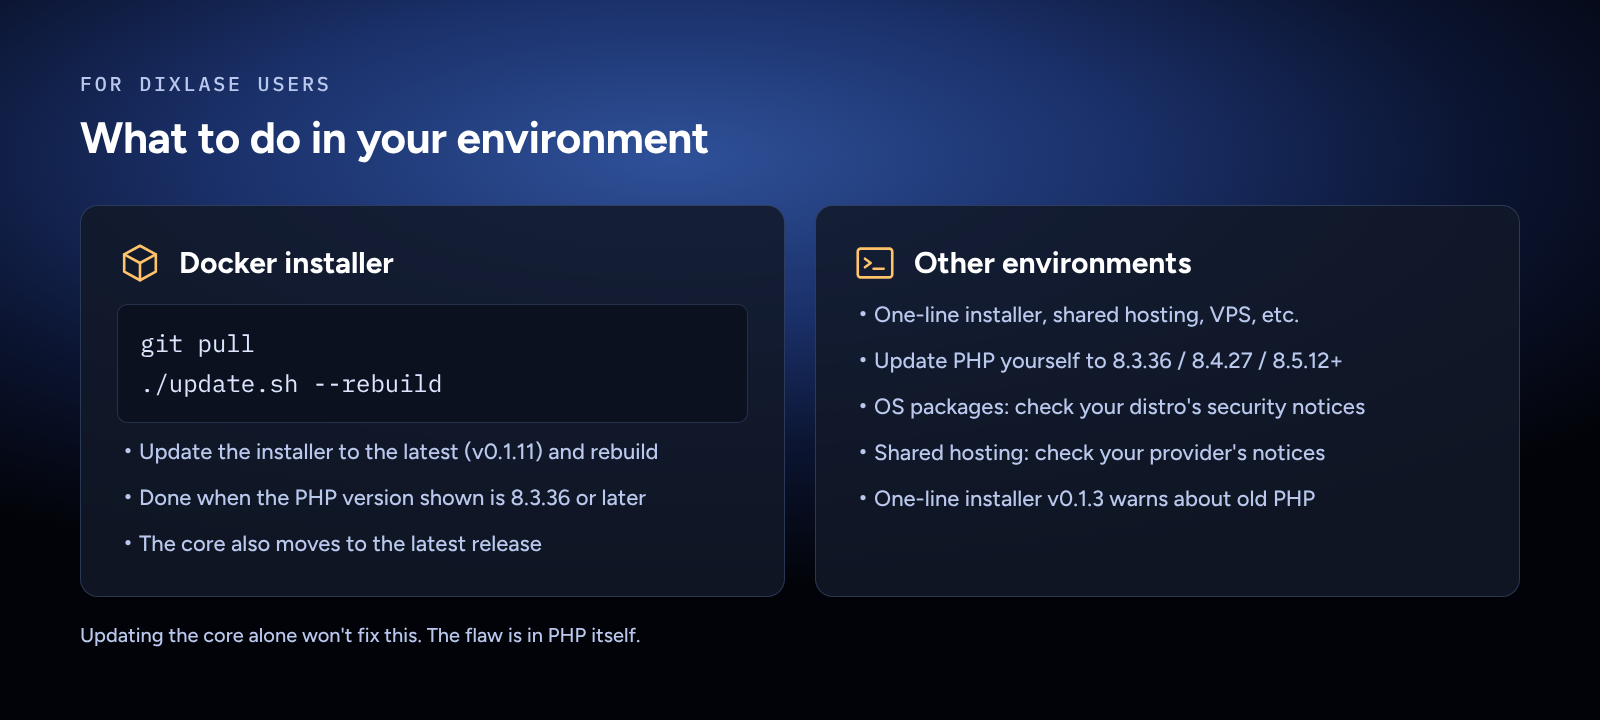
In your installer folder, run the following once. It brings the installer to the latest version (currently v0.1.11) and rebuilds the images with the new PHP.
git pull
./update.sh --rebuild
Every run shows the PHP version. Once it shows 8.3.36 or later, you're done.
Before updating, please also check the upgrade notes in the v0.1.10 release notes.
In other environments
Please update PHP yourself. If you use a hosting provider or a managed environment, please also check the notices from your provider.
If you can't update right away
PHP's security advisory lists stopgap measures (they are not a substitute for updating).
Of these, setting session.upload_progress.enabled = Off does not affect how Dixlase works. The Dixlase core, official plugins, and themes don't use this feature.
We've also improved our installers
In connection with these vulnerabilities, we've also improved how our installers work.
- Docker installer: It can now rebuild the images so PHP gets updated. If an update stops partway, the site keeps running as it was. (Latest: v0.1.11)
- One-line installer: It now warns during installation if PHP is older than these security releases. (v0.1.3)
Closing thoughts
This time, the vulnerability wasn't in a CMS but in PHP, the foundation underneath it. It affects not only Dixlase but every site and service that runs on PHP.
If anything about the update steps is unclear, feel free to let us know through a GitHub issue or on social media.
Update history
- 2026-10-[publication date]: Published